
Remove Duplicate APT Package Sources: Expert Guide for Ubuntu and Debian
Introduction: Why Double APT Sources Are a Problem
The Advanced Package Tool (APT) is the central tool for managing software packages in Debian-based distributions such as Ubuntu and Debian itself. The efficiency and reliability of APT depend directly on the integrity of the configured package sources. Over time, especially through the installation of third-party software, the use of Personal Package Archives (PPAs), or manual configuration errors, duplicate entries in package sources can occur.
While APT is generally robust enough to handle duplicate entries, redundant sources lead to unnecessary warning messages, slow down the update process ('apt update'), and can occasionally cause conflicts in package prioritization. For system administrators and advanced users, cleaning up these redundancies is an essential step towards maintaining a stable and efficient system. Therefore, removing double APT package sources is an essential practice of system hygiene.
Overview: Structure of APT Package Sources
To successfully identify duplicate entries, one must understand the hierarchical structure in which APT reads its configurations. APT reads package sources from two main areas:
1. The Main Configuration File (/etc/apt/sources.list): This file traditionally contains the primary repositories of the distribution (e.g., main, restricted, universe, multiverse in Ubuntu or main, contrib, non-free in Debian).
2. The Configuration Directory (/etc/apt/sources.list.d/): This directory contains separate `.list` files that are typically created by external installation scripts or PPA tools. Each of these files defines one or more specific repositories. This modular design facilitates management but is also the most common cause for duplications when a repository is manually entered into the main file and automatically added to a separate file.
A source is considered duplicate if the exact same URL, distribution (e.g., 'focal' or 'bullseye'), and component (e.g., 'main') are configured in two different lines or files.
Benefits of Cleaning Up Duplicate Sources
The systematic removal of redundant APT entries offers several operational and security benefits:
- Reduction of Error Messages: The most common sign of duplication is warnings that are displayed with every call to
apt update(e.g., 'W: Target Packages (main/binary-amd64/Packages) is configured multiple times'). Cleaning up eliminates these unnecessary outputs. - Faster Update Process: APT has to download and process the same metadata (package lists) multiple times from the server when duplicate entries exist. Removing duplicates reduces network load and processing time.
- Improved System Stability: Although APT handles duplicates, in complex scenarios, duplicate entries, especially if they have slightly different configurations, can lead to unpredictable behavior during package prioritization. A clean configuration minimizes this risk.
- Increased Clarity: An organized
sources.list.ddirectory makes manual inspection and management of external repositories easier, which is important for system security and maintainability.
Technical Details: Identification and Removal
The identification of duplicate sources always begins with running the update command as APT itself reports duplicates.
Step 1: Diagnose Using apt update
Run sudo apt update. Pay attention to all lines that start with 'W: Target...' and contain the hint 'is configured multiple times'. These warnings indicate which specific package lists (e.g., main/binary-amd64/Packages) are configured more than once.
Step 2: Manual Review of Configuration Files
The actual work requires a manual review of the relevant files. It is advisable to start by checking the directory /etc/apt/sources.list.d/, as most external sources are located there. Subsequently, the main file /etc/apt/sources.list is inspected.
Use a text editor with root privileges to open the files. Look for lines that show identical repository URLs, distributions, and components. A common pattern is that official distribution repositories are in sources.list, while a PPA or third-party repo is in a separate file in sources.list.d/.
Removal Strategy:
It is best practice to retain duplicates in the dedicated files in sources.list.d/ and remove or comment out redundant entries in the main file /etc/apt/sources.list. This ensures that management by automated scripts (often used by PPA tools) continues to work.
Caution During Removal: Never delete a file in sources.list.d/ unless you are certain all repositories within it are redundant. If you comment out a line in sources.list, ensure the corresponding source is still active in sources.list.d/.
Step 3: Validation
After redundant entries are removed or commented out, the process must be validated by running sudo apt update again. The warnings about duplicate sources should now be gone.
Use Cases: How Duplicates Occur
The management of APT package sources is a critical aspect of system administration under Debian and Ubuntu. While duplicate entries are often harmless, they signal poor system hygiene that can lead to unnecessary delays and potential conflicts.
1. Manual PPA Integration: A user wants to add a PPA. Instead of using the command add-apt-repository (which automatically creates a file in sources.list.d/), the user manually copies the repository line into /etc/apt/sources.list. Later, when the software is uninstalled and the PPA is removed via a tool that does not know about the manual entry in sources.list, duplication occurs if the user later re-adds the PPA.
2. Third-Party Installation Scripts: Some software vendors provide installation instructions that add the repository in two steps: first, manually adding the line to sources.list, then installing the key. If the vendor later provides an installation package that automatically creates a `.list` file in sources.list.d/, redundancy occurs.
3. Upgrade Processes: During major distribution upgrades (e.g., from Ubuntu 20.04 to 22.04), sources are often automatically adjusted. However, if older, no longer needed or duplicate third-party sources were not properly migrated or removed, they may appear as duplicates in the new system context, especially if they refer to the same old distribution.
Conclusion and Takeaway
The management of APT package sources is a critical aspect of system administration under Debian and Ubuntu. While duplicate entries are often harmless, they signal poor system hygiene that can lead to unnecessary delays and potential conflicts. The expert recommendation is to regularly review the sources, ideally after installing new third-party software or major system upgrades.
The clear takeaway for every system administrator is to rely on the modular structure in /etc/apt/sources.list.d/ and limit manual entries in /etc/apt/sources.list to official distribution sources. By consistently cleaning up duplicate APT package sources, you ensure that your system operates efficiently, quickly, and free of unnecessary warnings, significantly improving overall maintainability and stability.
Related Articles
Qwen 3.6 in Production: Release Runbook, AI Rollback, and LLMOps Versioning
Qwen 3.6 is not just another model upgrade. It is a release event, a rollback scenario, and a versioning problem at the same time. This article explains how Qwen 3.6 should be handled in production through LLMOps discipline, prompt and model traceability, controlled rollout, and evidence-based rollback readiness.
AI Agent Reliability: Why the Final Answer Is Not Enough
Correct output does not prove correct reasoning, safe execution, or a trustworthy system.
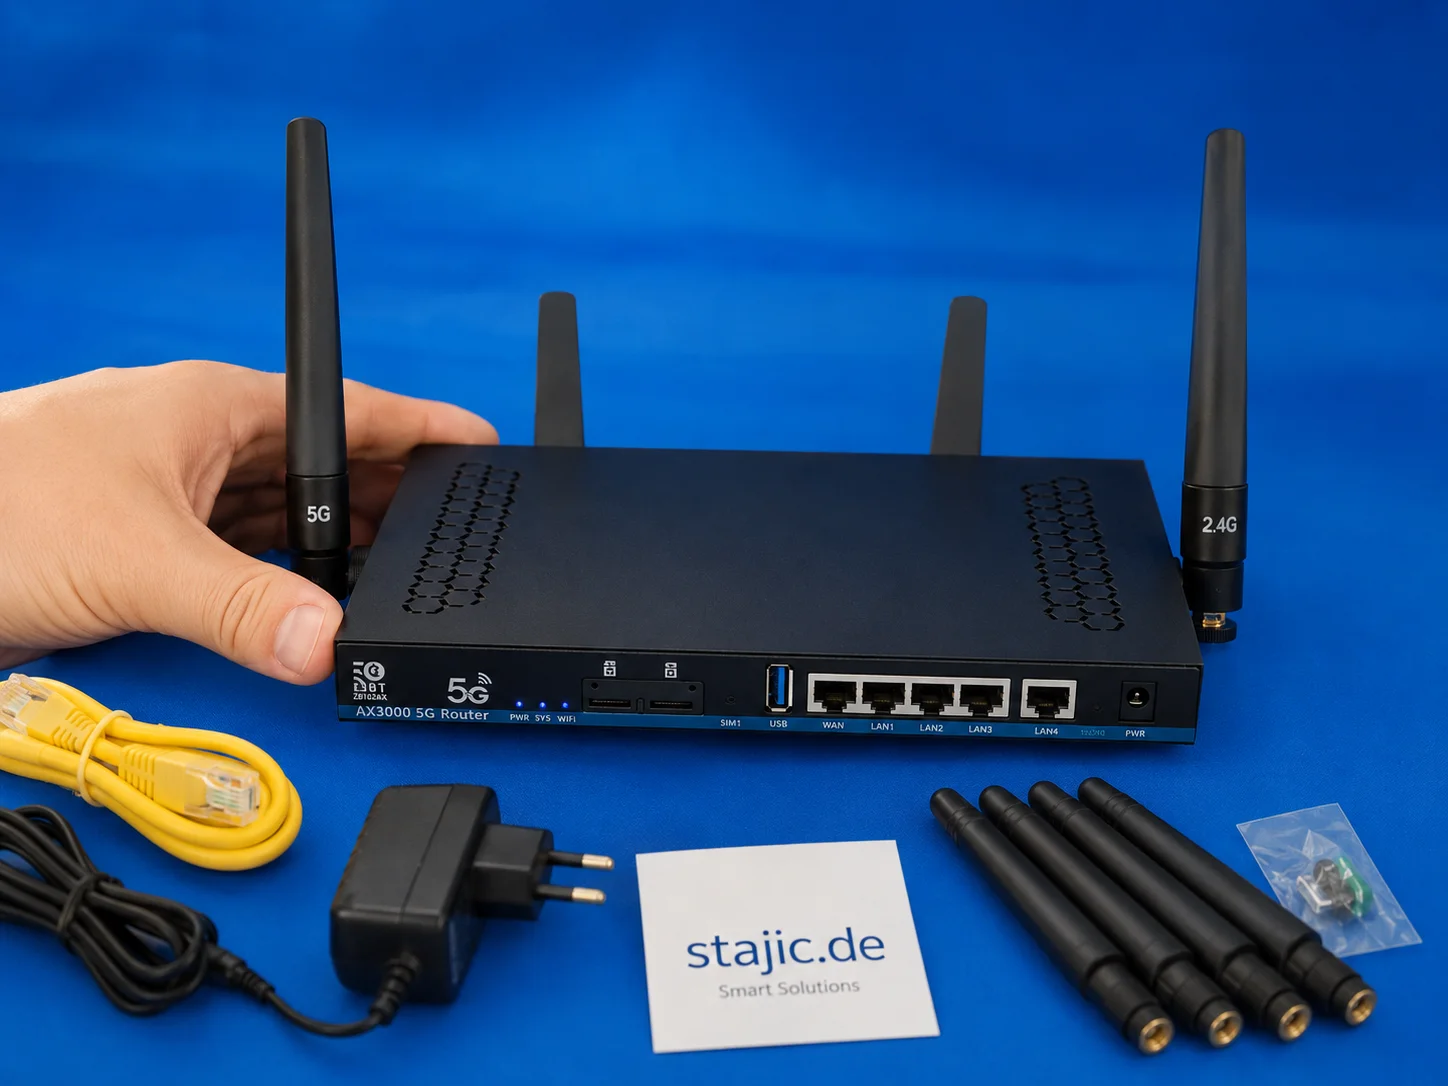
The Next OpenWrt 5G Router: Why Wi-Fi 7, a Stronger CPU and Better Firmware Matter
The ZBT Z8102AX is a useful first sample, but the next step should be stronger: Wi-Fi 7, a more powerful four-core platform, better firmware clarity, improved packaging and a more stable pricing policy. The goal is not just another 5G router, but a better configured OpenWrt-based prosumer device.
What Is Context Engineering? What the Model Receives Before It Answers
Context engineering designs what information an AI model receives before inference, including prompts, retrieval, memory, application state, tool results and conversation history.
OpenAI Agents API vs Agents SDK vs Responses API: What Should You Build On in 2026?
OpenAI’s agent stack changed in September 2026. This architecture guide separates the Agents API, Agents SDK, Responses API, and Codex SDK by runtime ownership—so teams can choose the right control boundary instead of comparing product names.
RBAC vs Tenant Isolation: Two Different Security Boundaries
RBAC controls what a user may do; tenant isolation controls which tenant’s resources that action may reach. Learn why multi-tenant SaaS security requires both boundaries.
What Is an AI Platform Architect? Models, Data, Runtime, Security and Operations
An AI Platform Architect designs reusable AI foundations across models, providers, retrieval, agents, identity, security, evaluation, observability and operations.
The GPU Is Not the Product: Future-Proof Private AI Architecture
Private AI infrastructure should not be designed around one GPU or one model. A more resilient approach combines fast inference GPUs, memory-rich AI systems, physical-AI nodes and optional frontier cloud models behind a capability-aware routing layer.
Google I/O 2026: Agentic Products Across Search, Workspace, and Shopping
Google I/O 2026 showed that agentic AI is moving beyond model demos and developer tools into everyday product surfaces. This article breaks down how Search, Workspace, Gemini Spark, and Universal Cart point toward a new product model where Google agents help users research, work, shop, and act across connected services.
Vector Databases, Embeddings and Reranking: Three Different Parts of Retrieval
Embeddings represent meaning, vector databases retrieve candidates, and rerankers refine results. Learn how these three retrieval layers differ and work together in RAG.
Google I/O 2026: Android XR, Intelligent Eyewear, and the Ambient AI Interface
Google I/O 2026 pushed Android XR and intelligent eyewear from concept toward a real platform direction. This article breaks down audio glasses, display glasses, Gemini-powered context awareness, developer implications, privacy risks, and why wearable AI is less about replacing phones and more about creating ambient assistance surfaces.
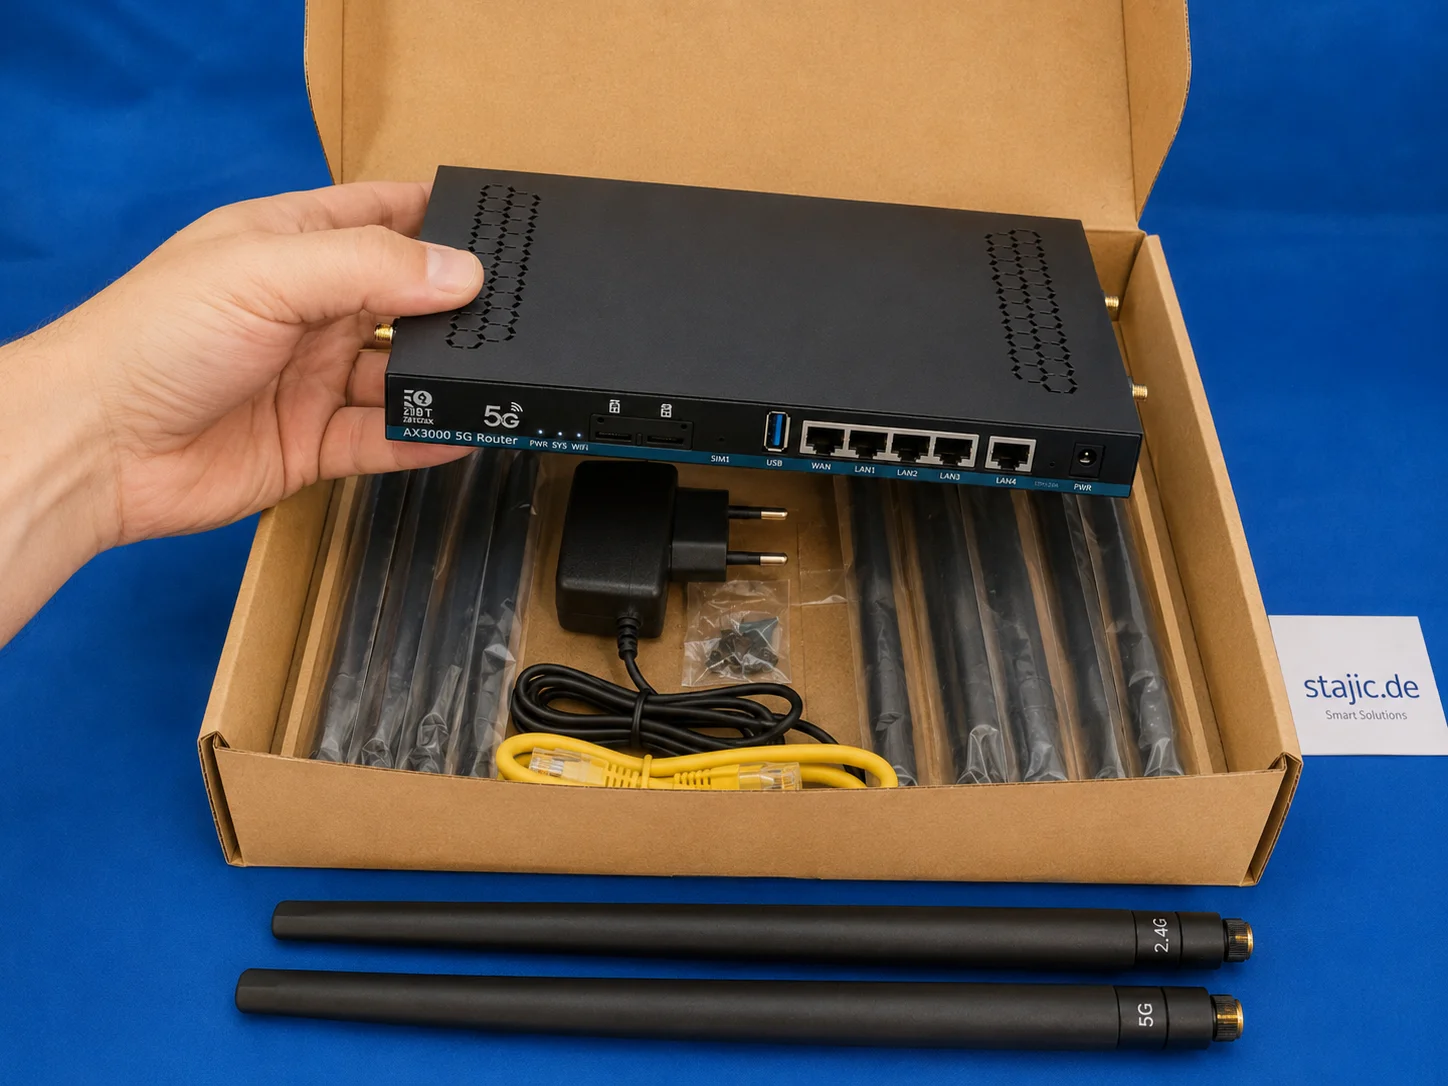
ZBT Z8102AX Hardware and Packaging Review: Strong Router, Weak Box
The ZBT Z8102AX makes a solid first impression as a slim black metal 5G OpenWrt router with multiple antenna connectors, dual-SIM slots, USB, LAN/WAN ports and a practical accessory set. The hardware feels useful and serious, but the packaging is clearly the weak point.